TL;DR

Get garage and car supplies delivered free — and shop member deals
- Fast, free delivery on millions of items
- Access to Prime Big Deal Days deals on October 6–7
- Prime Video, Amazon Music and more included
Researchers from Northeastern University and Consumer Reports tested network traffic from 21 late-model vehicles and 30 companion apps. They found that 19 vehicles contacted at least one third-party domain over Wi-Fi, while seven apps sent sensitive identifiers to third parties; the study does not establish how recipients used the data.
A study by Northeastern University researchers and Consumer Reports found that 19 of 21 late-model vehicles tested sent network traffic to at least one third party over Wi-Fi, while seven of 30 companion apps transmitted sensitive identifiers to third-party companies. The findings offer a measured look at data flows from connected cars and their phone apps, but do not show how recipients used the information after receiving it.
The team examined 21 vehicles from 19 brands and 30 manufacturer companion apps in a controlled setting between October 2024 and August 2025. Consumer Reports supplied access to its test fleet. Researchers monitored vehicle Wi-Fi traffic and used instrumented iPhones to capture and inspect app network traffic while exercising available functions.
In the vehicle tests, 19 of 21 cars contacted at least one third-party domain over Wi-Fi. The researchers could identify network destinations, but said vehicle traffic content was encrypted, limiting what they could read from those connections. The app tests found that seven of 30 apps sent personally identifying information to trackers or other third parties; five sent a vehicle identification number along with other personal information.
The report says the researchers tested vehicles while idle, during active use and on drives, and isolated cellular connectivity for a subset of 11 electric vehicles using a shielded enclosure. The project examined what data was transmitted and to whom. The findings describe observed traffic under those test conditions; they do not establish that every vehicle of a model behaves identically or that every destination used the data for advertising or resale.
What the Data Flows Reveal
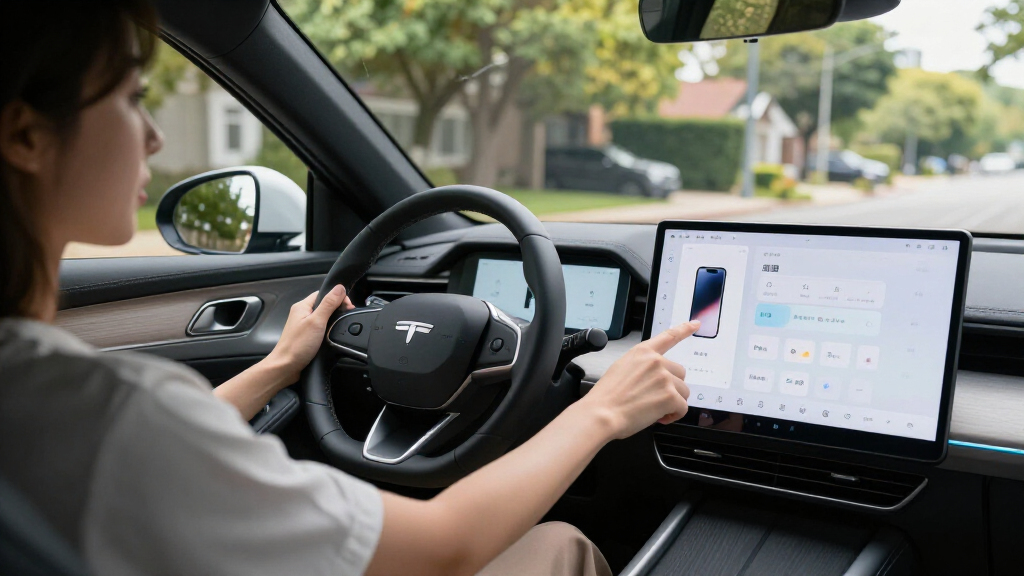
Connected vehicles and their apps can communicate with manufacturers and outside services as part of features such as remote access, location tools and charging searches. The study’s results show that third-party connections were common in the tested sample, and that some companion apps transmitted information the researchers classified as sensitive identifiers. That matters because vehicle and phone data can be linked to a person, a car or its movements.
The researchers stress a limit that is also central to the privacy concern: once data reaches a company, consumers may have little visibility into how it is retained, shared or used. The study measured transmission, not downstream handling. It therefore raises concrete questions for drivers about disclosure and control without proving that a particular recipient sold, misused or acted on the data.
For consumers, the findings may help explain why connected-car privacy is not only a matter of dashboard settings. Data can move through both the vehicle and its companion application, which may have separate permissions and service providers. The report supports continued scrutiny of those pathways, while leaving the scale of any resulting harm unquantified.
As an affiliate, we earn on qualifying purchases.
How Researchers Traced Car Traffic
A connected vehicle has internet-enabled services, often using cellular connections, Wi-Fi and GPS. Its manufacturer app can provide functions such as locating a car or checking vehicle information. The research team studied both sides of that arrangement because traffic from a car and traffic from a phone app may reach different company servers.
For vehicle Wi-Fi tests, researchers routed traffic through a custom access point built on a Raspberry Pi and recorded packet destinations. They could see where connections went, but encryption prevented inspection of the contents. For app tests, they used three iPhone models running different iOS versions, removed nonessential apps, and tested one vehicle app at a time. They accepted requested permissions and manually used each app’s available functions.
The researchers also placed 11 electric vehicles in a car-sized Faraday enclosure to block cellular signals and repeated stationary tests. This allowed them to examine whether traffic shifted to Wi-Fi when cellular service was unavailable. The study was conducted with a Consumer Reports fleet, which the research site says would have cost more than $1.2 million to assemble independently.
““Consumers have no control over their data once it has left their device.””
— Northeastern University research team
What the Tests Cannot Establish
The study does not identify the eventual use of every observed data flow. In particular, a connection to a third-party domain does not by itself show that information was sold, used for targeted advertising or shared onward. The researchers say that, after data is sent, its handling depends on the receiving companies; the tests did not follow all downstream transfers or decisions.
The findings also reflect 21 vehicles and 30 apps tested under defined conditions, not every connected vehicle on the road. The vehicle traffic was encrypted, so researchers could record destinations but not read all transmitted content. The report does not provide enough detail in the supplied material to assess how each manufacturer responded to the researchers’ disclosure process, or whether any company changed its practices.
Peer Review and Manufacturer Responses
The research team says the paper is peer reviewed and will be published at IMC ’26. The study’s findings and methods may receive further scrutiny through that publication. The team also describes a disclosure process with manufacturers, but the supplied report does not list individual responses or say whether companies have committed to specific changes.
Further measurement could test more vehicle models, software versions and app updates, and examine how data practices change over time. Until then, the results are best read as evidence of observed third-party connections in this sample—not as a complete map of the connected-car industry or proof of what happened to each data point after transmission.
Key Questions
What did the connected-car study find?
Researchers found that 19 of 21 vehicles contacted at least one third-party domain over Wi-Fi, and seven of 30 companion apps sent personally identifying information to third parties.
Does the study prove car companies sold driver data?
No. The tests measured network traffic and identified destinations, but did not establish how each recipient used the data or whether it was sold or shared onward.
Could researchers read everything sent by the cars?
No. Vehicle traffic was encrypted. The team could record destinations for Wi-Fi connections, but could not inspect the contents of those vehicle packets.
Which vehicles and apps were tested?
The researchers tested 21 late-model U.S.-market vehicles from 19 brands and 30 related companion apps. The supplied findings do not name the individual brands or apps.
What happens next with the research?
The team says the paper is peer reviewed and is scheduled for publication at IMC ’26. The report does not specify a publication date or disclose detailed responses from individual manufacturers.
Source: hn
Fall Picks
fall essentials
As an affiliate, we earn on qualifying purchases.